This guide shows how to build a non-hackable crypto exchange, or more honestly, an exchange that is very hard to hack and that loses little if someone gets in. No team can promise zero risk. What you can do is stack layers of defence, so that one stolen password, one bad server or one tricked employee is never enough to empty your wallets.
We start with the real hacks of 2025 and 2026, because they show where attackers actually get in. Then we walk through the wallet setup, the web and app protections, the people risks and the checks you need before launch. By the end, you will know which controls to build first and what to ask any team that builds your exchange.
In this guide:
- Why “non-hackable” really means risk reduction, and what that looks like in practice
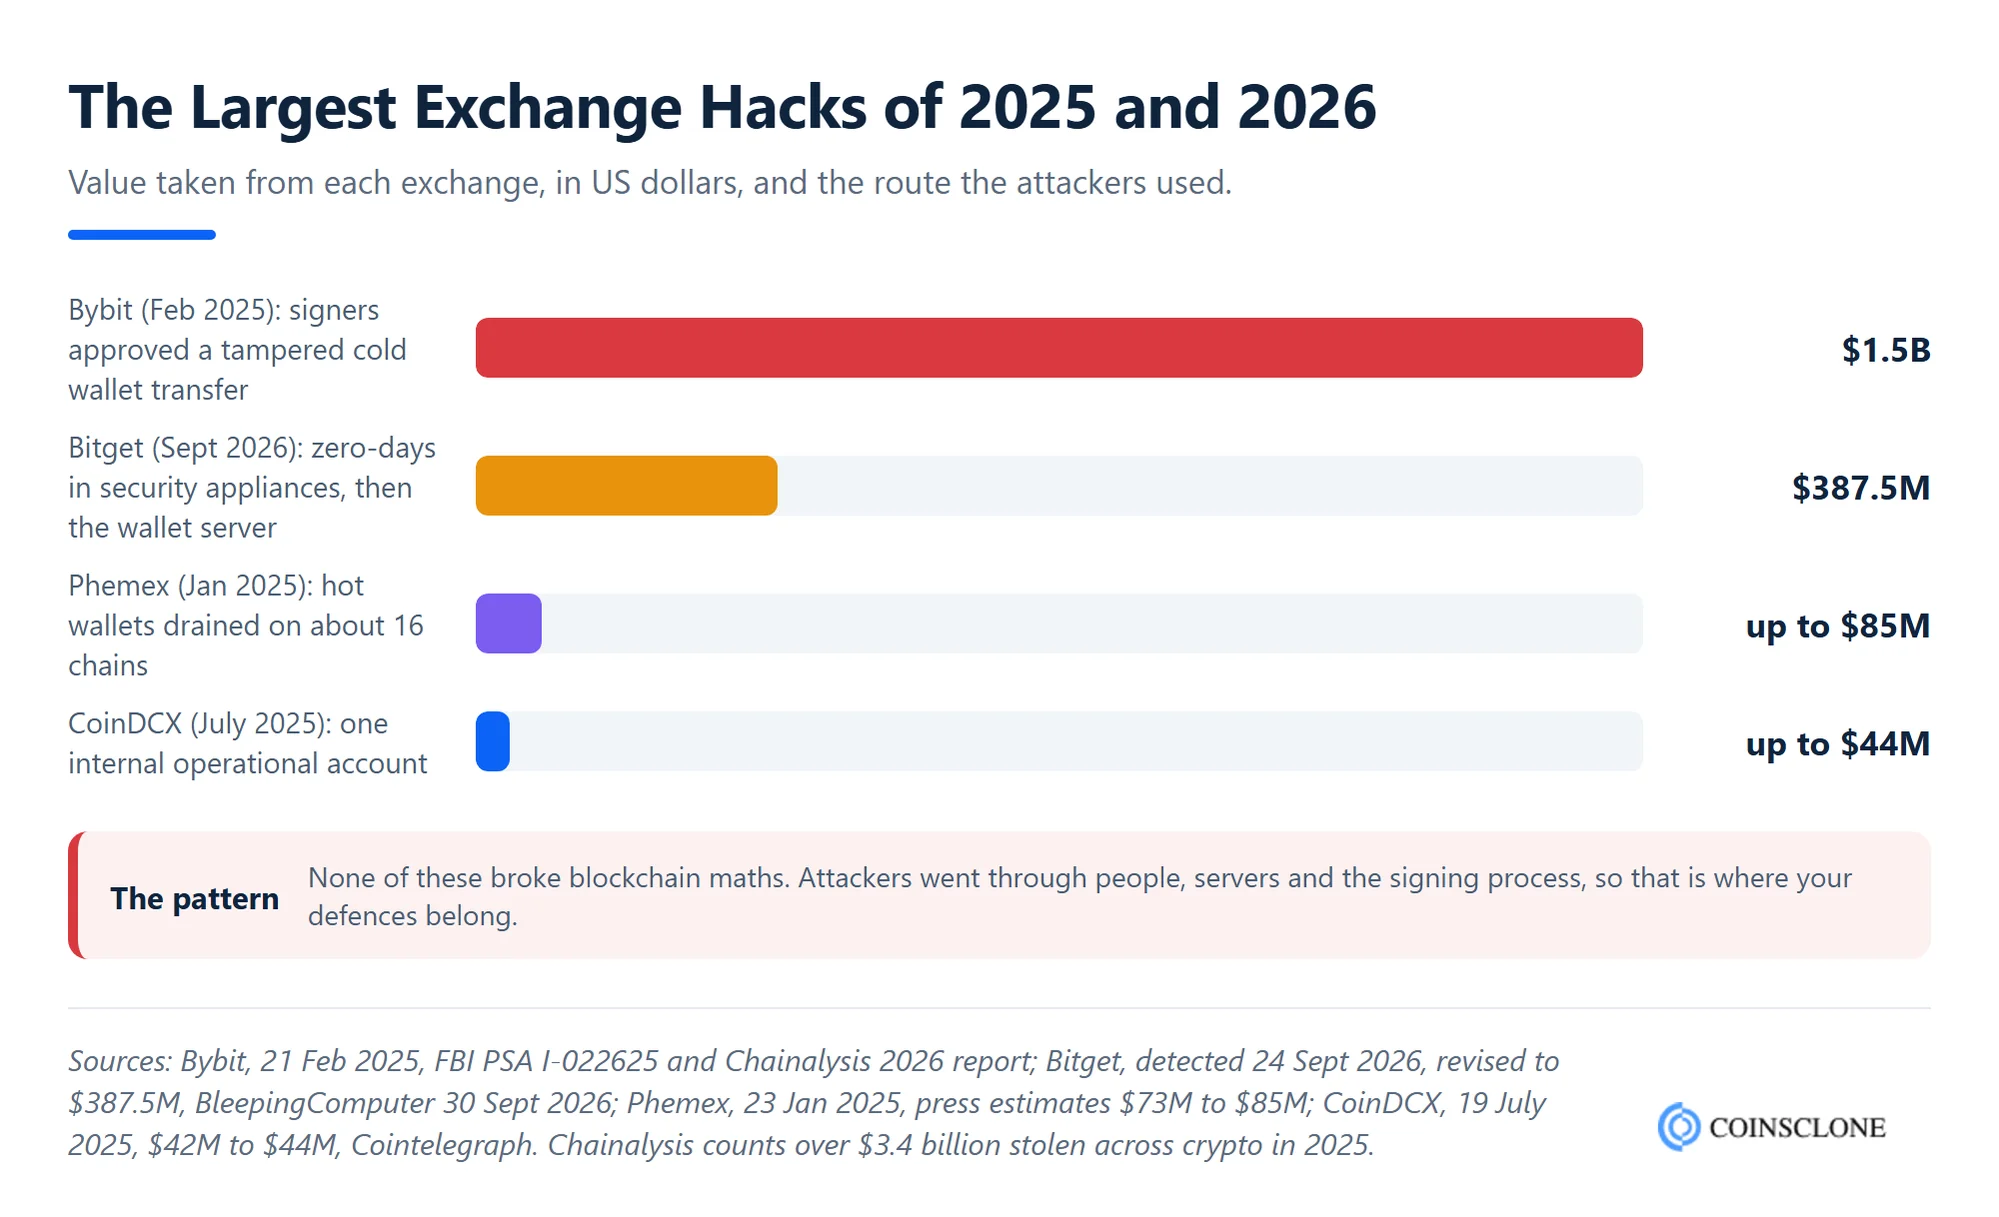
- What the Bybit ($1.5 billion) and Bitget ($387.5 million) hacks teach a new exchange
- How to set up hot, warm and cold wallets with MPC or multisig signing
- The web, app and staff protections every exchange needs in 2026
- A short checklist to run before your exchange takes its first deposit
Build a Non-Hackable Crypto Exchange — Fast!
Your exchange deserves bulletproof security and blazing speed.
- Iron-Clad Security: Multi-layer protection, no exploits.
- Secure Wallets: Cold + hot wallets with auto-shield tech.
- Instant Liquidity: Plug-and-play pools, no coding required.
- Custom Branding : Your logo, UI, and trading pairs.
Get a free branded security demo in 48 hours — before you invest a cent.
Book a Free Demo and see how our next-gen system helps you launch a non-hackable crypto exchange in 8 to 12 weeks.
How to Build a Non-Hackable Crypto Exchange
To build a non-hackable crypto exchange, you protect three things at once: the keys that move funds, the servers that talk to those keys and the people who approve transfers. Blockchain maths is rarely the weak point. Instead, attackers go after logins, servers, support staff and the signing process.
So the goal is not a wall that can never fall. The goal is a set of layers where each one can say no, and where a breach in one layer stays small. Here is the order we follow:
- Keep most funds offline: Store the bulk of assets in cold storage and keep only a small float in hot wallets.
- Split signing power: Use MPC or multisig, so no single person, device or server can move funds alone.
- Check every transfer twice: Add a separate system that reads each transfer and compares it with the request before anyone signs.
- Lock down accounts: Use 2FA or passkeys, withdrawal whitelists and a time lock on new addresses.
- Harden the web app and APIs: Block SQL injection, CSRF, SSRF and DDoS attacks, and encrypt data at rest and in transit.
- Limit insider and vendor risk: Give staff the least access they need, vet hires and review each outside tool.
- Watch, test and prepare: Monitor outflows in real time, run audits and pen tests, publish proof of reserves and rehearse your response plan.
The sections below explain each layer, starting with the hacks that shaped them.
What is a Cryptocurrency Exchange?
A cryptocurrency exchange is a trading platform where users buy, sell and swap cryptocurrencies. Exchanges earn from trading fees, listing fees, withdrawals and more, which is why so many startups launch one. However, a centralized exchange also holds its users’ coins. That makes it a single, rich target, so you need strong security and thorough testing before the business goes live.
Also Read :- The Steps Involved in Starting a Cryptocurrency Exchange
Why Top Security Matters in a Crypto Exchange
The first reason is money. In 2025, hackers stole more than $3.4 billion in crypto, and the February attack on Bybit alone took $1.5 billion, Chainalysis reports. North Korean groups took at least $2.02 billion of that total, up 51% on 2024. The pace has not slowed in 2026: blockchain security firm CertiK counted $1.26 billion lost across 247 incidents in the third quarter alone.
The second reason is trust. Users move to exchanges they believe are safe. After a hack, many leave and few come back, even when the exchange repays them. Some never recover at all: Mt. Gox collapsed in 2014, and a hack can still end a young exchange today.
The third reason is the law. In the EU, crypto firms now need a MiCA licence, and the EU’s DORA rules ask licensed firms to manage ICT risk, test their systems and report major incidents. Other regulators expect the same basics. So security is no longer only good practice. It is part of getting and keeping a licence.
Case Studies of Hacking in Crypto Exchanges
Exchange hacking began in 2011 with Mt. Gox, the first big exchange to be attacked, and it has never stopped. The cases below show how the methods have changed, from simple hot wallet thefts to attacks on the people and systems that approve transfers.
Coincheck (2018)
In January 2018, hackers took about $530 million in NEM tokens from Coincheck, a large Japanese exchange. The coins sat in a hot wallet that was always online and protected by a single key, with no multisig. Coincheck repaid users and was later bought by Monex Group, but the case pushed Japan to tighten its exchange rules.
BitMart (2021)
On 4 December 2021, thieves used a stolen private key to drain two BitMart hot wallets, one on Ethereum and one on BNB Smart Chain. Security firm PeckShield put the loss at about $196 million, while BitMart gave its own figure as about $150 million. BitMart said it would cover user losses. Its later troubles had other causes: it announced a wind-down on 26 July 2026, ended all trading on 26 August 2026 and is now in a restructuring.
FTX (2022)
FTX did not fail because of a hack. It failed because user funds were misused, and it filed for bankruptcy in November 2022. However, within a day of the filing, more than $400 million was drained from its wallets in unauthorised transfers. The lesson: during a crisis, when staff and systems are under stress, wallet controls matter most.
Bybit (2025)
On 21 February 2025, hackers took about $1.5 billion in ETH from a Bybit multisig cold wallet. They did not break the wallet’s code. Instead, they faked the signing screen. The signers saw a normal transfer, but they approved a change that handed control to the thieves. The FBI tied the theft to North Korea. Bybit stayed open and covered the loss, but the case proved that cold storage and multisig fail if signers cannot trust what their screens show.
Coinbase (2025)
In May 2025, Coinbase said crooks had bribed support staff abroad to copy user data from its help desk tools. The data covered less than 1% of monthly users, and no passwords, keys or funds were taken. Coinbase refused a $20 million ransom, yet it estimated the cost of fixes and refunds at $180 million to $400 million. Attackers used the stolen data to trick users into sending them funds.
Bitget (2026)
On 24 September 2026, Bitget spotted unauthorised transfers from its hot and warm wallets. The loss was first put at $351.6 million and later revised to $387.5 million. Per Bitget’s own probe, hackers used unknown flaws (zero-days) in two security boxes bought from other firms. From there they reached the server that runs wallet jobs and fed it fake transfer data. Bitget’s own approval system then moved the funds. Bitget paused withdrawals, restored them in stages from 28 September and said its protection fund covers the loss.
What These Hacks Have in Common
Look closely and a pattern appears. None of these attacks broke blockchain cryptography. Each one went through a hot wallet with too much money in it, a single key, a person who could be tricked or bribed, or a server that the signing system trusted too much. That is good news for builders, because every one of those weak points can be designed out. This is also why owning a crypto exchange platform can be safe and profitable, as long as security is part of the plan from day one.
Wallet and Key Security: Where Most Exchange Losses Start
The largest losses come from the wallet layer, so build it first. Here are the controls that matter most.
Hot, Warm and Cold Wallet Tiers
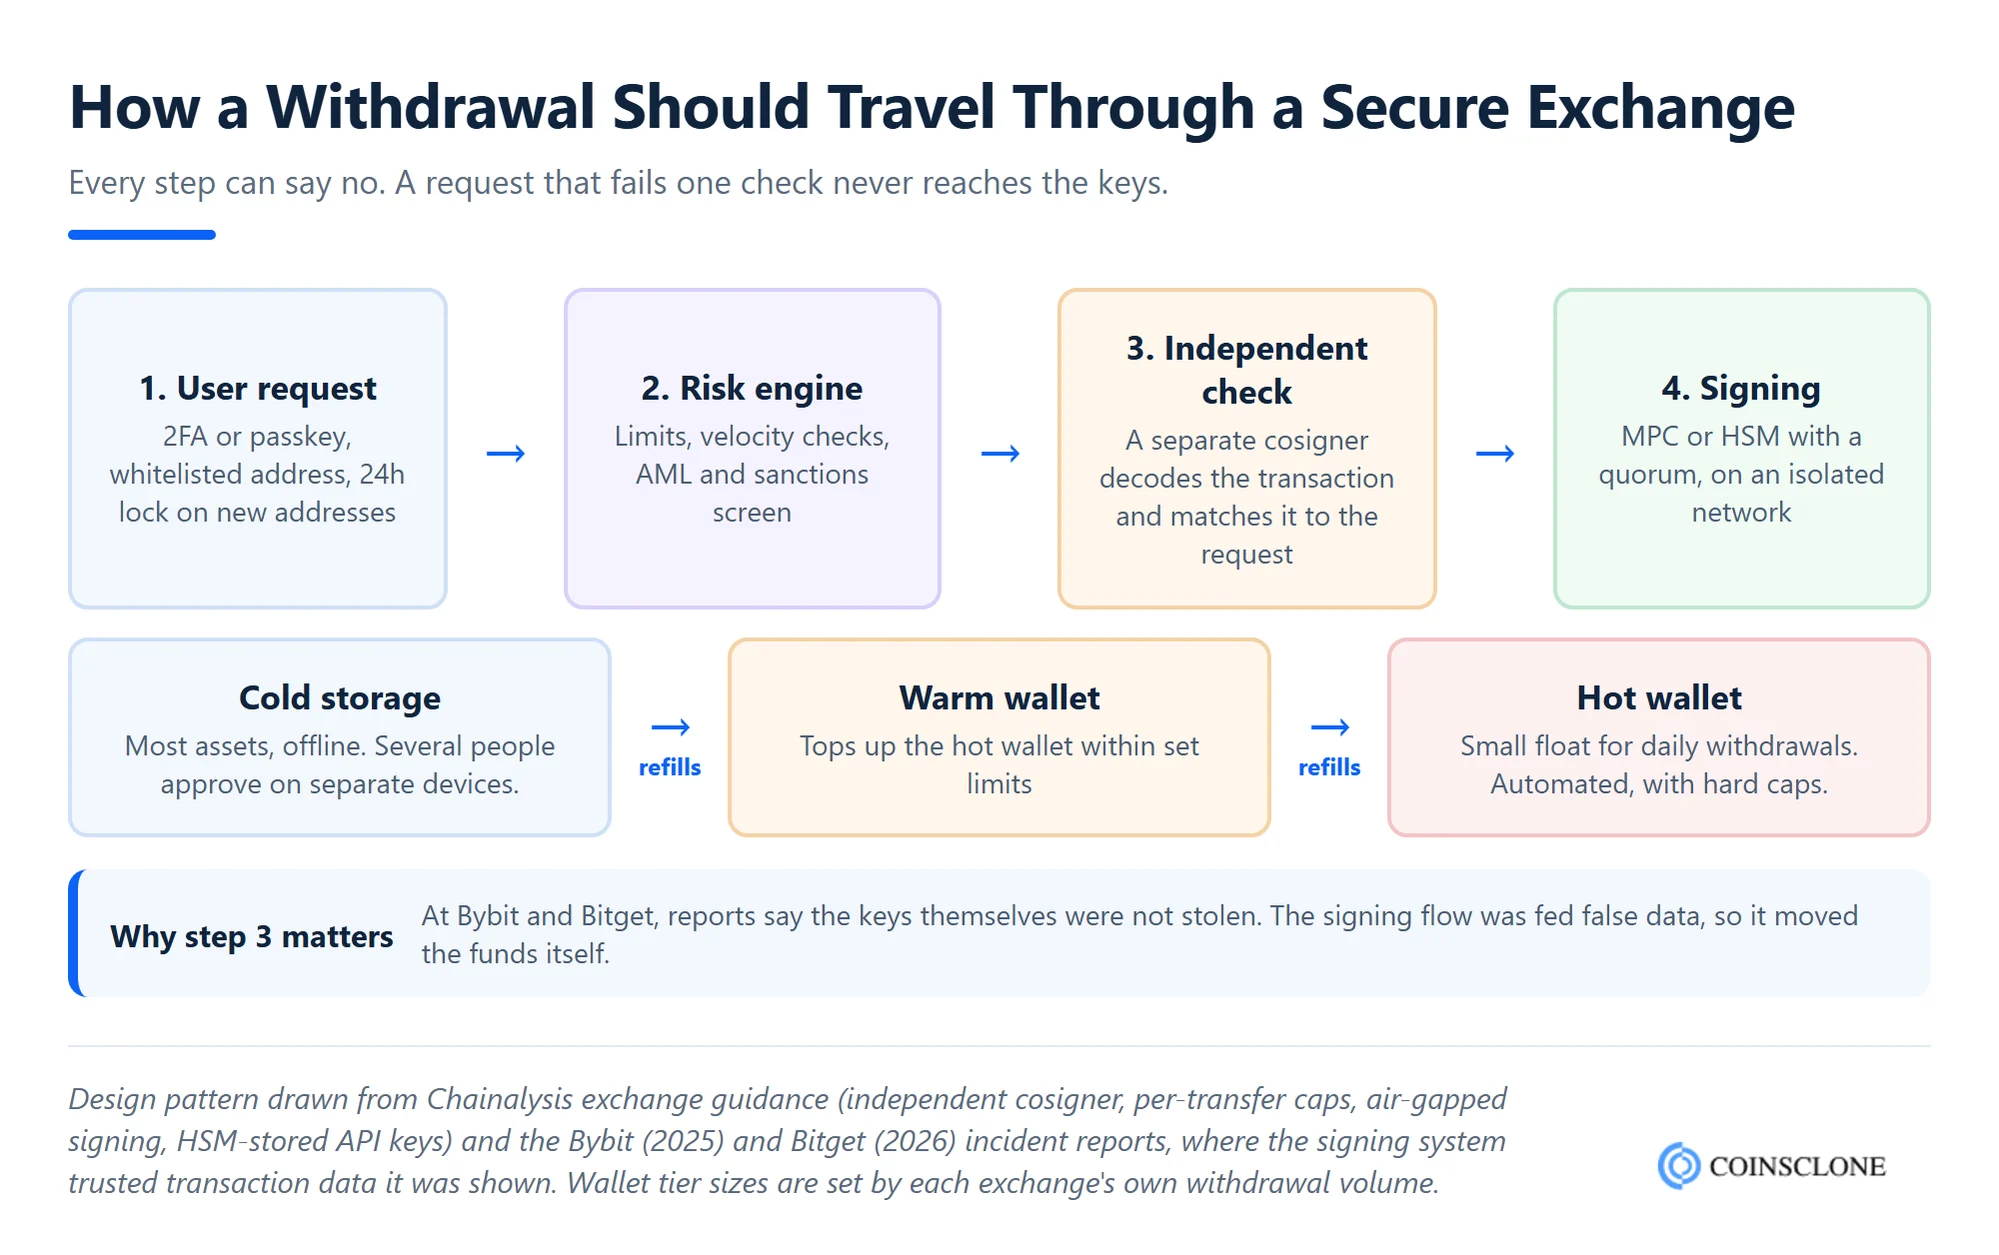
Keep most assets in cold storage, offline and away from the internet. A warm wallet tops up the hot wallet within set limits, and the hot wallet holds only what users need for daily withdrawals. Size the hot wallet from your real withdrawal data, then set hard caps on it. If the hot wallet is drained, the loss stays small and the cold reserve stays safe. Our guide to the types of crypto wallets explains each wallet type in more depth.
MPC or Multisig Signing
With multi-signature (multisig) wallets, several keys must approve each transfer, such as 2 of 3 or 3 of 5. With multi-party computation (MPC), one key is split into shares that sign together, so the full key never exists in one place. Either way, no single person, laptop or server can move funds alone. Keep signing devices on an isolated network and use them only for signing. If you want this layer built for you, see our MPC wallet development service.
An Independent Check Before Signing
Bybit and Bitget both had multi-step approvals. Still, in both cases the signers or systems acted on false data. So add a second check that works on its own. It reads each transfer, compares it with the first request and blocks it if the two do not match. Large transfers should also be confirmed on a second, trusted device. Chainalysis also advises a cap on any single transfer, so one bad approval cannot empty a wallet.
Withdrawal Rules
Give every withdrawal a set of rules to pass. Common ones are:
- Address whitelists: Users can withdraw only to addresses they saved earlier.
- Time locks: New addresses or changed security settings trigger a 24 to 48 hour hold.
- Limits and speed checks: Daily caps per user, plus alerts on many withdrawals in a short time.
- AML screening: Check destination addresses against sanctions lists and known hack wallets.
Keys and Secrets Storage
Never keep private keys, API secrets or database passwords in code or plain text files. Store them in a hardware security module (HSM) or a secrets vault, and rotate them on a schedule. Then even a stolen copy of your code or database does not give an attacker the keys.
Security Features That Need to Be Included in a Crypto Exchange
The exact mix differs for each business. Still, developing a Crypto exchange Company means strong app and network safety is a must. Cutting corners here leads straight to account takeovers and data leaks. Here are the features every exchange should ship with.
Secure Login and Sessions
Login is the front door of your exchange. Use strong password rules, rate limits on login attempts and short-lived sessions that end after inactivity. A basic HTTP login alone is not enough today. Pair the password with a second factor and alert users to each new device or place.
End-to-End Encryption
Most users know end-to-end encryption from WhatsApp. It protects messages between two parties, so no one in the middle can read them. On an exchange, the same idea means using TLS (HTTPS) on each link between apps, servers and partners. Then no one can read or change data on the way.
Data Encryption
Data encryption turns readable data into coded text that only the right key can unlock. Encrypt databases, backups and identity documents at rest, using a standard such as AES-256. If these features feel daunting, talk to skilled MVP developers of crypto exchange software before you build.
Two-Factor Authentication
Two-factor authentication (2FA) cuts the risk of stolen passwords. Even if one password leaks, the second factor keeps the account safe. App-based codes, passkeys or hardware keys are safer than text messages, because attackers can hijack phone numbers through SIM swaps. Ask for 2FA again on withdrawals and security changes, not only at login.
SQL Injection Prevention
SQL injection is a code attack that lets hackers read or change data in your database, often through website forms or APIs. You can prevent it with parameterized queries that bind typed values, careful use of stored procedures and strict input checks.
Cross-Site Request Forgery (CSRF) Protection
CSRF tricks a logged-in user, through an email or link, into sending a forged request to your server. It works against sites that use cookies for login, because browsers send cookies with every request. CSRF tokens and same-site cookie settings block these attacks.
Server-Side Request Forgery (SSRF) Protection
In an SSRF attack, a hacker makes your server send requests to internal systems that should be off limits. Features that fetch data from URLs are the usual target. Block unused URL schemes, allow only approved destinations and keep wallet servers on a separate network that web servers cannot reach.
Anti-Denial of Service (DoS)
A denial of service attack floods your platform so real users cannot reach it. Splitting the network into smaller segments, rate limiting and request filters help stop it. With anti-DoS in place, users can trade without slowdowns.
Anti-Distributed Denial of Service (DDoS)
A DDoS attack uses many machines at once to flood your exchange. It can freeze trading at the worst moment, and attackers sometimes use one to hide a theft. A DDoS protection service at the network edge, backup capacity and a tested failover plan keep the exchange online.
API Security
Traders and bots use your APIs every second, so APIs are a frequent target. Give API keys narrow rights, such as keys that can trade but not withdraw. Tie them to approved IP addresses and rate limit each endpoint. For a full list of trading, wallet and admin tools, see our guide to the features of a cryptocurrency exchange.
People, Insiders and Vendor Risk
Many of the costliest attacks start with a person, not a bug. Coinbase lost customer data through bribed support staff. Bitget was breached through flaws in security tools it bought from other vendors. And per Chainalysis guidance for exchanges, the US has charged 14 North Koreans over fake remote IT jobs that earned more than $88 million. So fake job seekers are a real risk too.
Here is how to limit these risks:
- Least access: Each staff member gets only the access their job needs, and support staff never see full identity data or wallet controls.
- Vetting: Run background checks, verify remote hires on live video and watch for odd network activity.
- Training: Teach staff to spot phishing and social engineering, since many hacks start with one clicked link.
- Vendor review: List every third-party tool, patch it fast and keep it outside the network that holds wallet systems.
- Logs: Record every admin action, so you can spot misuse quickly and trace it later.
Monitoring, Audits and Your Response Plan
Prevention will never be perfect, so plan to catch problems fast and limit the damage.
- Real-time monitoring: Track outflows and alert the team on unusual amounts, new addresses or odd hours. Bitget’s attackers were active for weeks before the theft, which shows the value of early detection.
- Audits and pen tests: Hire an outside firm to test the code, wallets, APIs and cloud setup before launch, then repeat after major changes and at least once a year.
- Bug bounty: Pay outside researchers who report flaws to you first.
- Proof of reserves: Publish regular proof, such as a Merkle tree check, so users can confirm their coins are backed one to one. Note that proof of reserves shows backing, not security.
- Protection fund: Keep a reserve to repay users after a loss, as Bybit and Bitget did.
- Response plan: Decide in advance who pauses withdrawals, who talks to users and how you trace and freeze stolen funds with other exchanges.
Security Standards and Rules to Follow in 2026
Standards give your team a shared checklist and give partners and regulators proof of your work. The most useful ones for exchanges are:
- OWASP ASVS: The OWASP Application Security Verification Standard lists the checks a web app should pass.
- ISO 27001 and SOC 2: Common frameworks for running data security as a process. Banks and partners often ask for them.
- CryptoCurrency Security Standard (CCSS): A set of rules for key creation, storage and signing in crypto systems.
- MiCA and DORA (EU): The MiCA rules require a licence to run an exchange, and the transition periods ended by 1 July 2026. DORA adds ICT risk, testing and incident reporting duties. Our guide to launching a MiCA-compliant white label exchange in the EU covers the steps.
Pre-Launch Security Checklist
Before your exchange takes its first deposit, make sure you can tick every line below.
| Area | Check before launch |
| Wallets | Most funds in cold storage; hot wallet capped; MPC or multisig on every tier |
| Signing | Independent transaction check; large transfers confirmed on a second device |
| Accounts | 2FA or passkeys; withdrawal whitelists; time locks on new addresses |
| App and APIs | OWASP checks passed; API keys scoped; rate limits on every endpoint |
| Network | DDoS protection; wallet servers isolated from web servers |
| People | Least access; vetted staff; phishing training done |
| Testing | Outside audit and pen test closed out; bug bounty live |
| Response | Monitoring alerts tested; incident plan rehearsed; protection fund set |
How Our Clone Scripts Can Solve the Problem?
Since major crypto exchanges have faced hacks, we have studied the weak spots that need the most care. Our crypto exchange clone scripts ship with these layers built in. They include cold and hot wallet tiers, multisig or MPC signing, 2FA, withdrawal checks, data coding (encryption), DDoS shields and admin roles. They can also be customized to fit your business, and they have been tested across many launches.
Because the core is ready, a clone script costs far less and launches far faster than a build from scratch. Our white label crypto exchange software typically goes live in 4 to 6 weeks, 7 to 10 weeks with fiat rails and 9 to 13 weeks with mobile apps. Coinsclone has been building since 2018 and has delivered 350+ platforms for 200+ clients across 20 industries. Even so, we always recommend an outside security audit before launch, because no script or team can promise zero risk.
Also Read :- How much does it cost to build a crypto exchange
Conclusion
Hackers will always look for a way in, and no exchange can be truly non-hackable. However, you can make attacks hard, slow and small. Keep most funds offline, split signing power, check every transfer twice, protect accounts and APIs, and watch your people and vendors as closely as your code. The 2025 and 2026 hacks show that the costliest failures happen in the signing process and in the human layer, so build those with the most care. Join hands with Coinsclone, and our cryptocurrency exchange development services will help you launch an exchange with these security layers from day one.
Build a Non-Hackable Crypto Exchange — Fast!
Your exchange deserves bulletproof security and blazing speed.
- Iron-Clad Security: Multi-layer protection, no exploits.
- Secure Wallets: Cold + hot wallets with auto-shield tech.
- Instant Liquidity: Plug-and-play pools, no coding required.
- Custom Branding : Your logo, UI, and trading pairs.
Get a free branded security demo in 48 hours — before you invest a cent.
Book a Free Demo and see how our next-gen system helps you launch a non-hackable crypto exchange in 8 to 12 weeks.
Frequently Asked Questions
Can a crypto exchange be hacked even with cold storage and multisig?
Yes. Cold storage and multisig cut the risk a lot, but they are not magic. In February 2025, hackers took about $1.5 billion from a Bybit multisig cold wallet by faking the screen the signers used. So you also need an independent check of each transaction and a trusted second device for large transfers.
How can I prevent a crypto exchange from being hacked?
You cannot rule out every attack, but you can make one hard and keep its damage small. Keep most funds offline and use MPC or multisig signing. Add a second, separate check before signing. Then require 2FA and saved withdrawal addresses, harden your web app and APIs, limit staff access and test the platform with outside audits.
How do crypto exchanges protect private keys?
Exchanges keep most keys offline in cold storage and split signing power with MPC or multisig, so no single person holds a full key. API secrets and hot wallet keys sit in hardware security modules or secrets vaults, never in code. Signing devices run on isolated networks and are used only for signing.
How can a crypto exchange prevent unauthorised withdrawals?
Use withdrawal whitelists, time locks on new addresses, daily limits, speed checks and AML screening. Ask for 2FA on each payout. Then add a separate system that compares each transfer with the user’s request before signing. Bitget’s 2026 loss came from fake transfer data fed to its approval flow.
What happens to users’ crypto if an exchange is hacked?
It depends on the exchange. Bybit in 2025 and Bitget in 2026 covered losses from their own reserves and reopened withdrawals in days. Weaker exchanges may freeze withdrawals for months or shut down, and users then become creditors. This is why proof of reserves and a protection fund matter.
Does proof of reserves mean a crypto exchange is secure?
No. Proof of reserves shows that an exchange holds enough assets to back user balances at a point in time. It does not show how well those assets are guarded. It is a useful trust signal, but it should sit alongside audits, cold storage and strong signing controls.
How often should a crypto exchange undergo security testing?
Run a full outside audit and pen test before launch, after any major change to wallets or code, and at least once a year. Between those, use automated scans, a bug bounty and real-time monitoring, so new flaws are found quickly.