You’ve built your crypto payment gateway. Now, how do you protect it? This guide gives you 12 practical tips to secure a crypto payment gateway in 2026, from cold storage and signed webhooks to address screening and an incident plan. Each tip says what the threat is, what the fix looks like and where it sits in your build.
The stakes are high. Hackers stole more than $3.4 billion from crypto services in 2025, and in September 2026 a single breach at Bitget cost about $387.5 million. So we also cover the risks behind those losses, the 2026 rules your gateway must follow and a short test list to run before you go live.
In this guide:
- 12 tips to secure a crypto payment gateway, each tied to a real threat
- Where attacks hit a gateway, layer by layer, and the control for each
- A four-step check that decides when a payment is safe to credit
- The 2026 rules that shape gateway security: MiCA, the Travel Rule, the GENIUS Act and more
- A pre-launch security checklist you can hand to your team
See How Our Proven System Can Secure Your Crypto Payment Gateway
Crypto Payment Gateway Development — done right.
-
Advanced Security Stack : Multi-sig wallets, 2FA, SSL, and DDoS protection by default.
-
Compliance-Ready : Built-in KYC/AML modules to meet global regulations.
-
Fraud Prevention : Real-time monitoring and risk scoring to block suspicious transactions.
-
Data Protection : End-to-end encryption for all payment and user data.
Get a free security audit checklist to evaluate your payment system’s safety.
Book a Free Demo to learn how our Crypto Payment Gateway Development Solution helps you launch faster — and safer.
How to Secure a Crypto Payment Gateway: 12 Tips for 2026
Building a crypto payment gateway is one thing; keeping it secure in today’s threat landscape is another. As the value and volume of crypto payments grow, you need a layered approach. In other words, no single tool should be the only thing standing between an attacker and your funds.
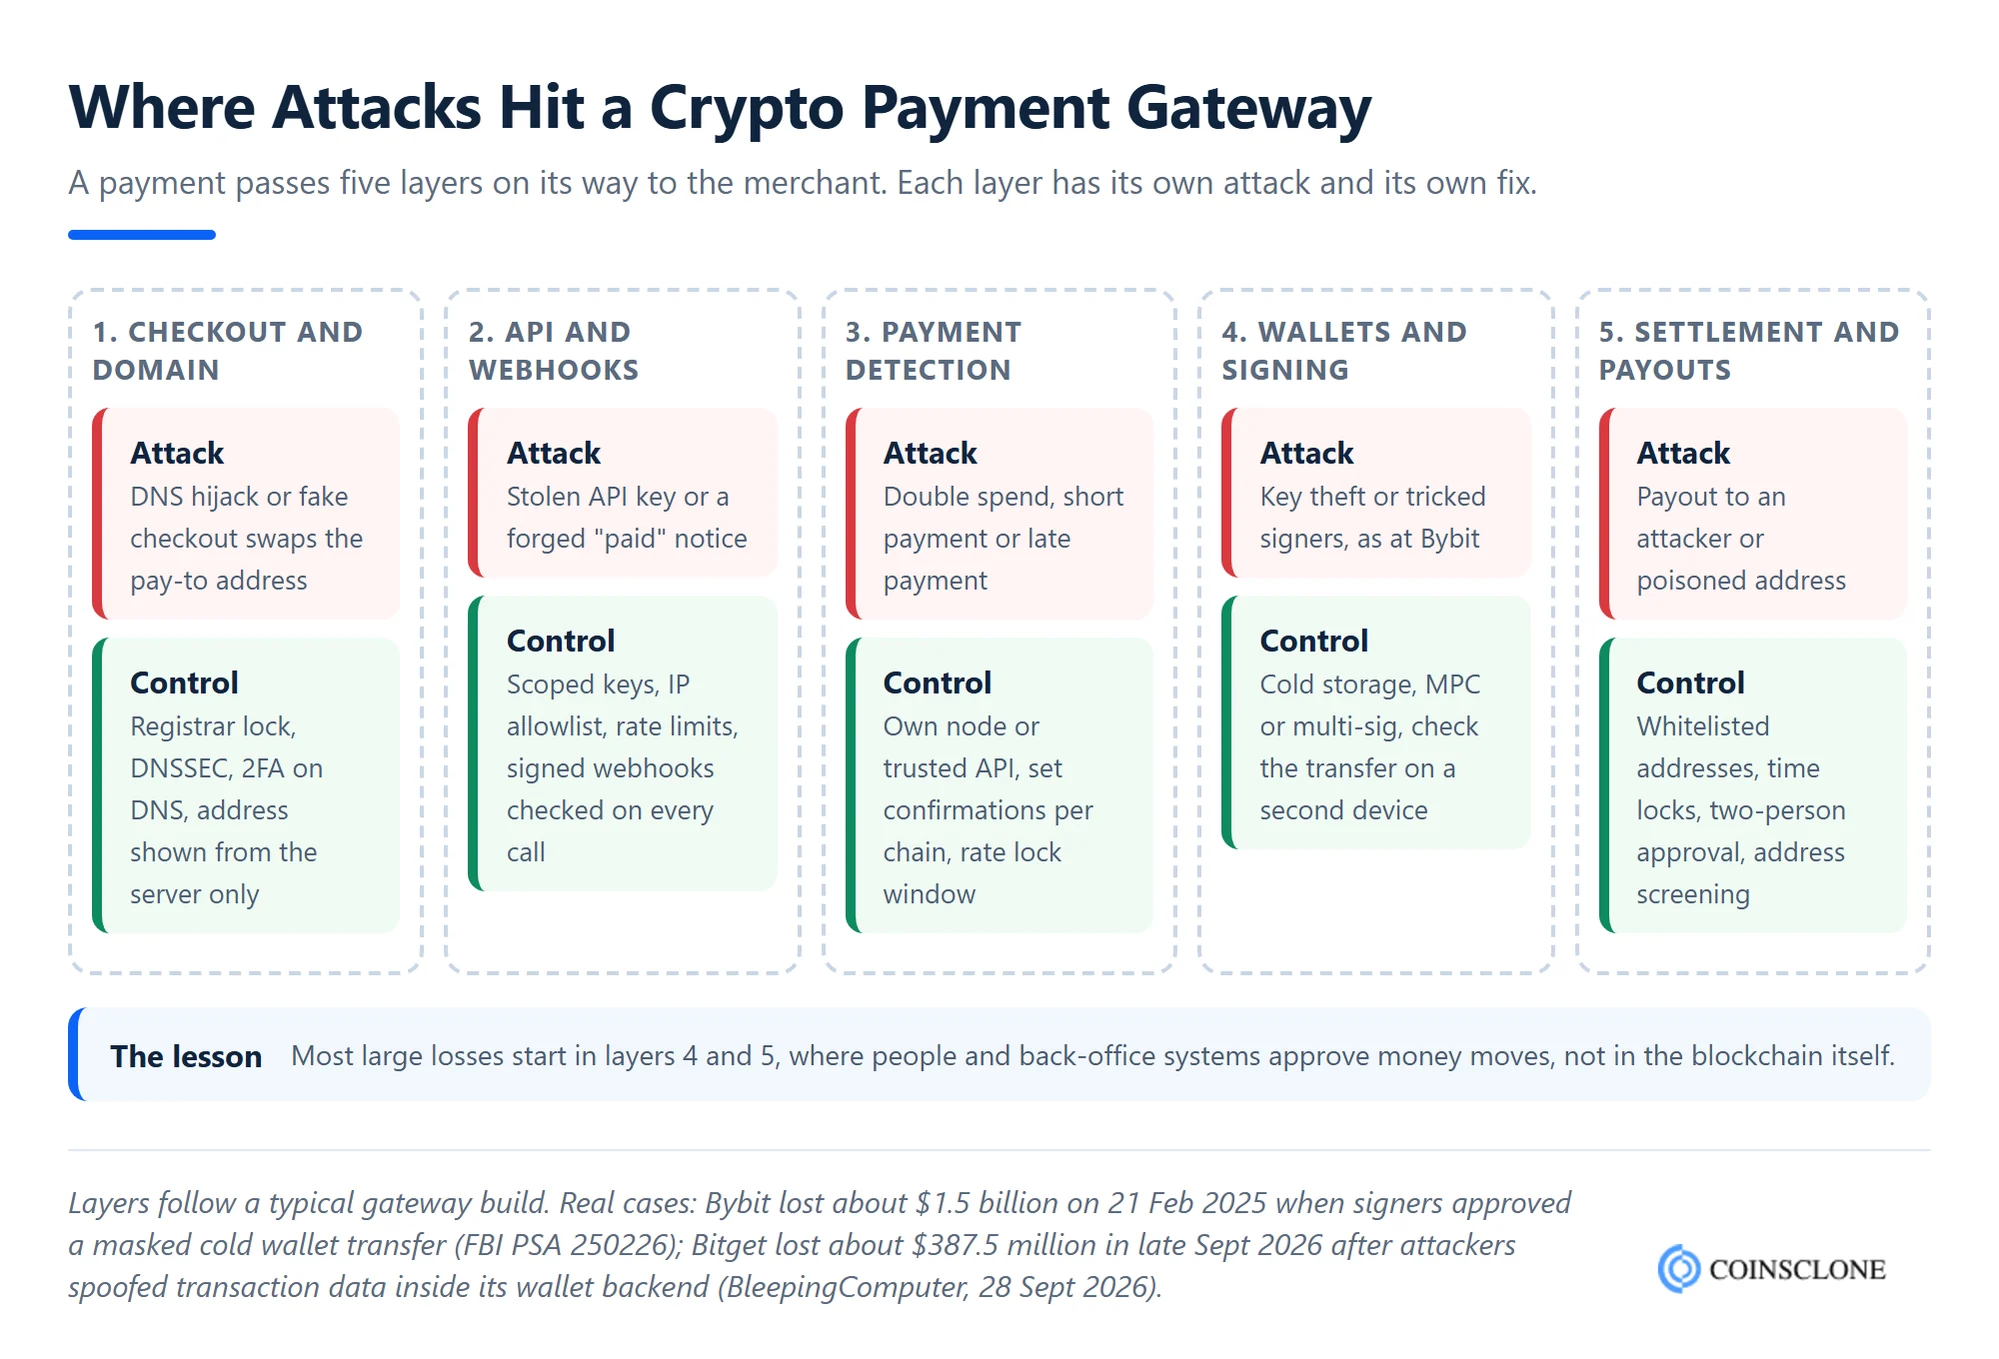
A payment passes through five layers on its way to the merchant: the checkout page, the API, payment detection, the wallets and the payout step. Each layer has its own attack and its own fix, as the diagram below shows. The 12 tips that follow cover all five.
1. Run Audits Early and Often
Security isn’t static. Regular audits help you find weak spots before attackers do. Hire outside security firms to run pen tests (mock attacks), smart contract reviews and checks of your servers and cloud setup.
Plan a full audit before launch and after every major release. Then add smaller checks each quarter. As a result, new code and new chains never go live without a second pair of eyes on them.
2. Implement Multi-Layer Encryption
Encryption is your first line of defense against data theft. Use strong standards such as AES-256 for stored data, private key backups and user details. Then use TLS 1.2 or later for each connection, even calls between your own services.
Above all, never keep private keys or API secrets in your code or in plain database fields. Store them in a secrets vault or a hardware security module (HSM). Then even a stolen copy of your database is useless.
3. Use Cold Storage, Multi-Sig or MPC, and Two-Factor Login
Keep only the funds you need for daily payouts in hot wallets. Store the rest offline in cold storage. Then split signing power with multi-signature (multi-sig) wallets or MPC, so that no single person, laptop or server can move funds alone. Our MPC wallet development guide explains how key shares work.
Next, add two-factor authentication (2FA) to each login. An app or a hardware key is safer than a text message. Finally, check what you sign. In February 2025, attackers took about $1.5 billion from Bybit, and the FBI tied the theft to North Korea. The signers saw a normal-looking cold wallet transfer while the logic underneath had changed. So confirm large transfers on a second, separate device before anyone approves them.
4. Check Each Payment On-Chain and Sign Each Webhook
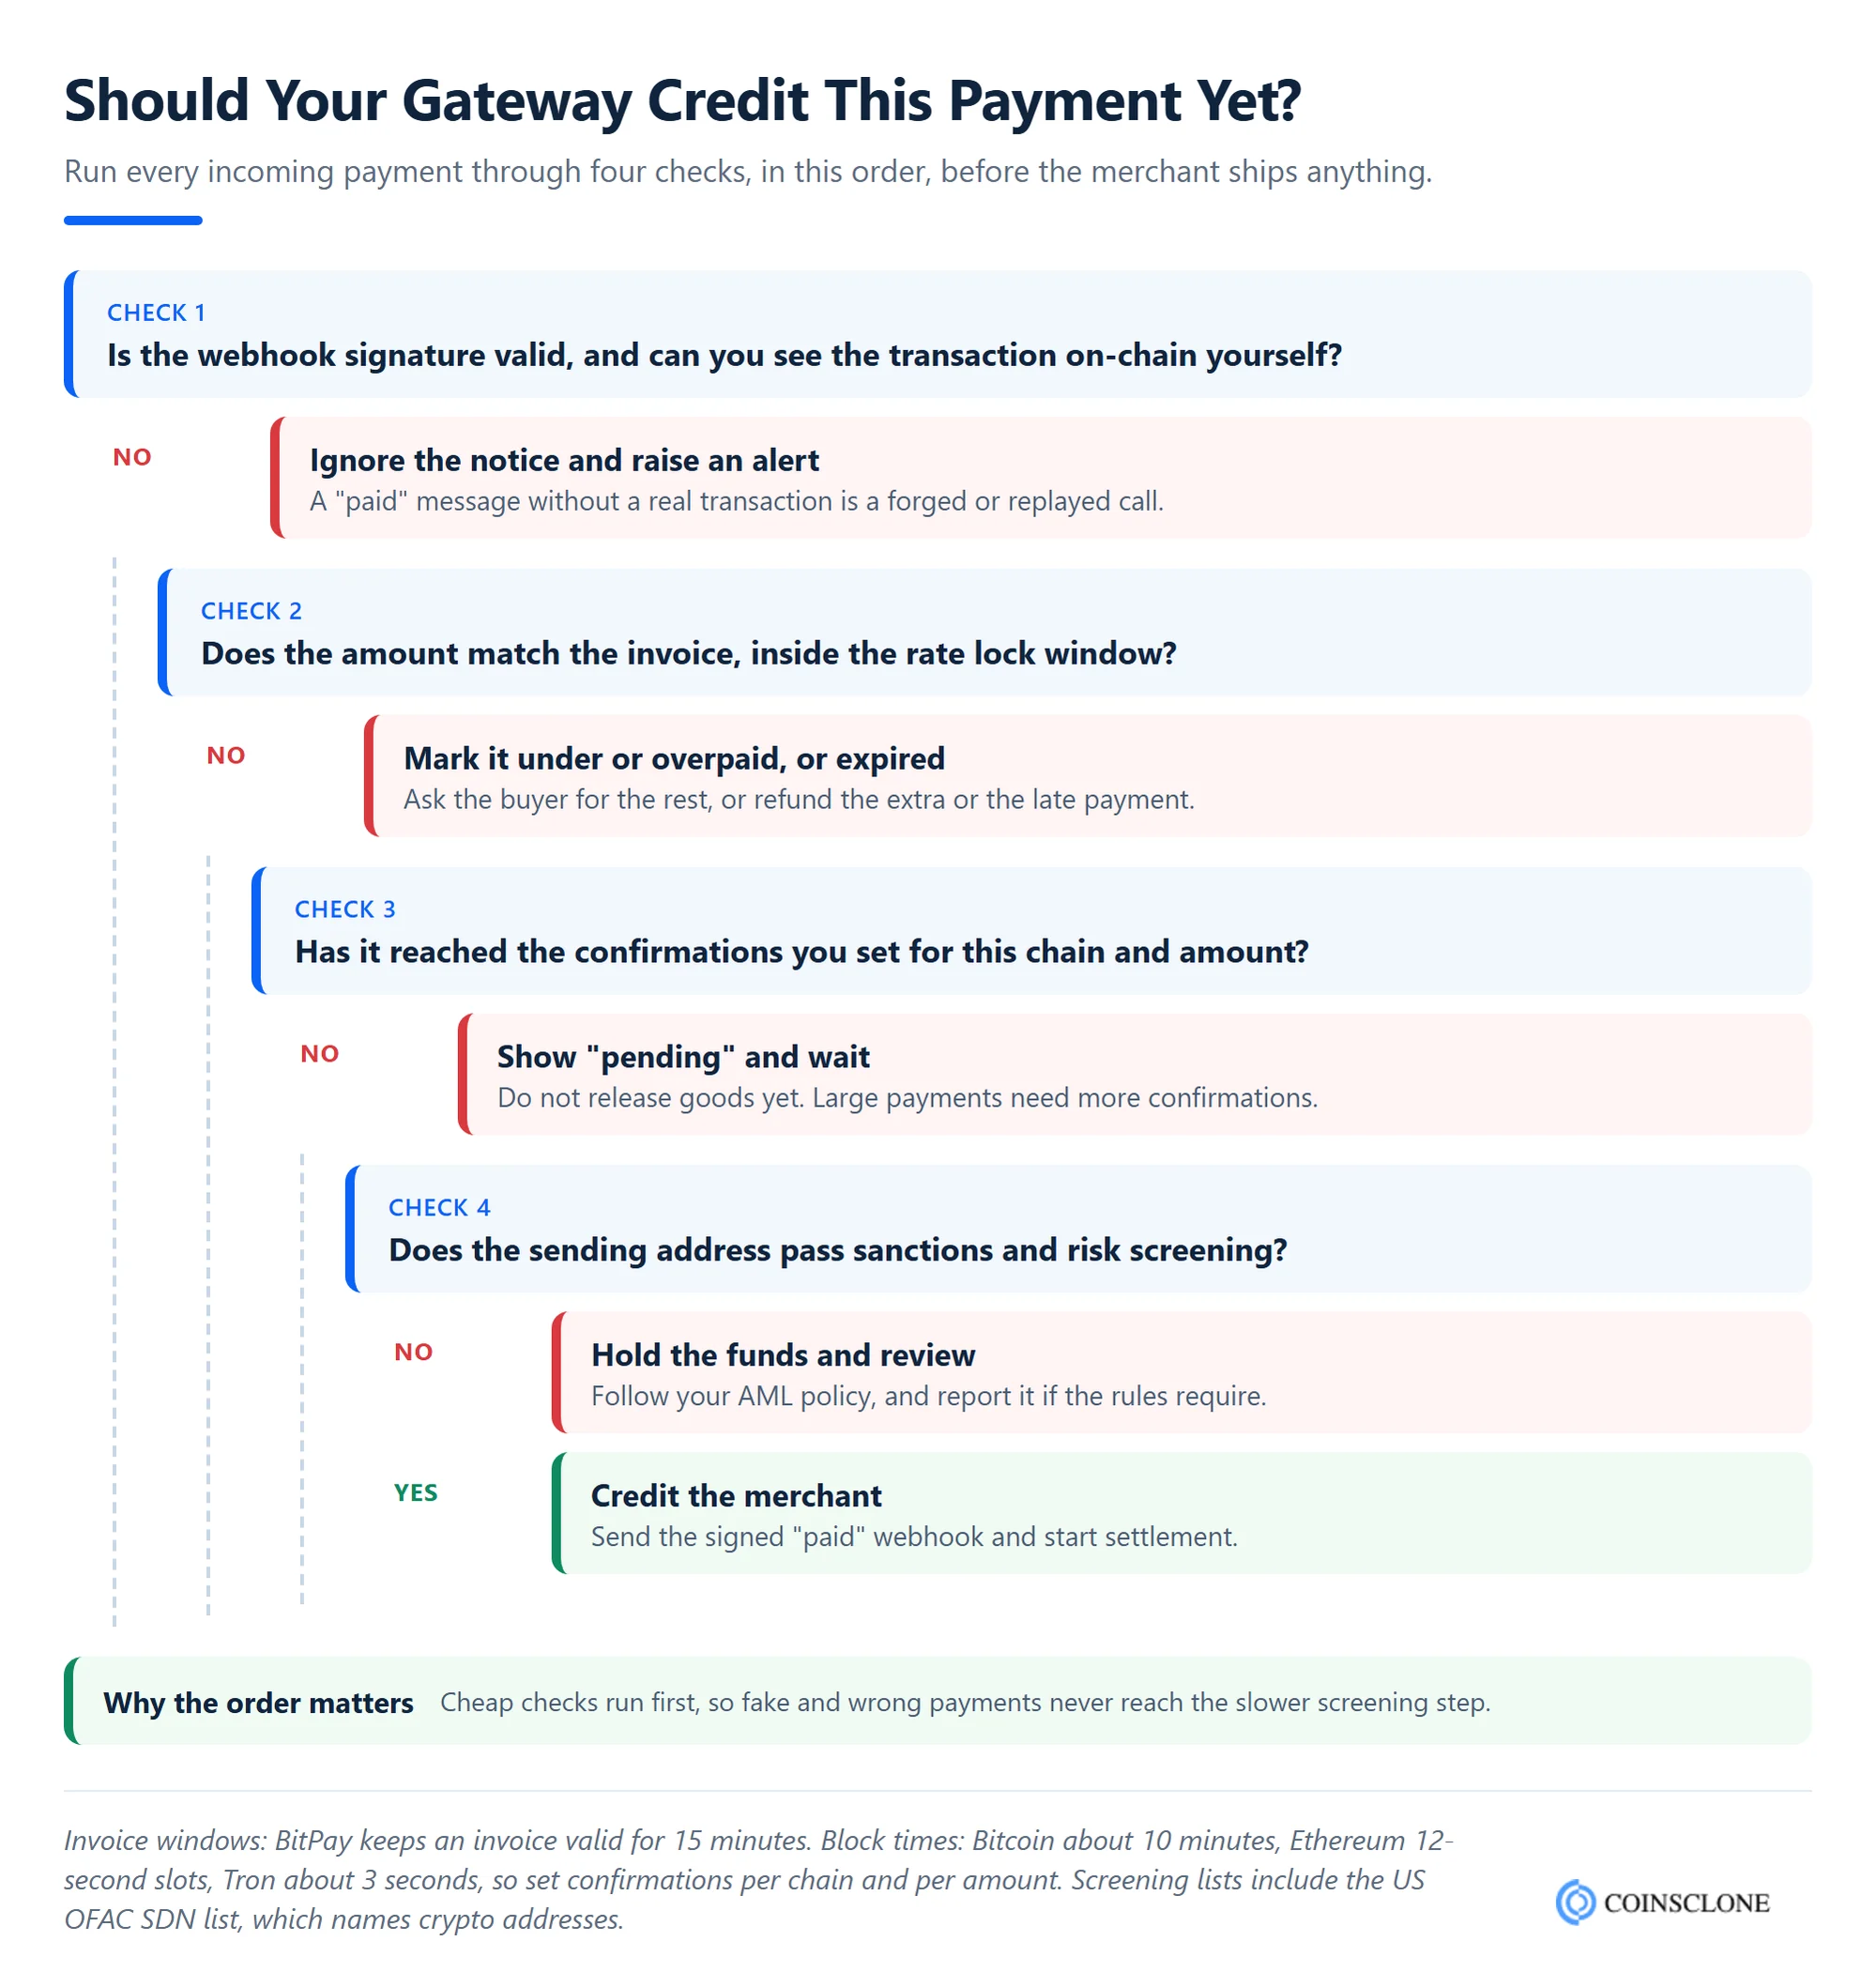
A gateway’s main job is to say “this order is paid”. Attackers know this, so they try to fake that message. Never trust a payment status sent from the buyer’s browser. Instead, confirm each payment on-chain through your own node or a trusted provider.
Then sign each webhook you send to merchants, for example with an HMAC code and a timestamp. That way, their stores can reject forged or replayed calls. Also set the number of confirmations per chain and per amount. A Bitcoin block takes about 10 minutes, while an Ethereum slot takes 12 seconds, so one rule for all chains does not work. The decision tree below shows the order of checks.
5. Watch for Fraud in Real Time and Screen Addresses
Use live monitoring tools, powered by AI and on-chain data, to spot trouble at once. Look for odd payment patterns, sudden fund movements, many small payments from new wallets or repeated failed logins. Early detection lets you respond fast and limit the loss.
In addition, screen incoming and outgoing addresses against sanctions lists, such as the US Treasury’s OFAC SDN list, and against known hack and scam wallets. This matters for stablecoins too. Issuers such as Tether and Circle can freeze USDT or USDC at a flagged address. So if you take tainted funds, your own balance can get stuck.
6. Enforce KYC, KYB and AML Compliance
Rules are getting stricter worldwide, so KYC and AML checks are a must. KYC means you know who your customer is, and AML means you watch for dirty money. Verify each merchant before they go live (KYB), and verify buyers where the law requires it. These checks stop fake accounts and illegal payments.
Compliance also builds trust with banks, partners and merchants. Keep clear records of each check, since regulators and auditors will ask for them. We cover the main rules by region in the compliance section below.
7. Harden Your API and Server Security
APIs are the backbone of crypto payment systems and a prime target for hackers. Give each merchant scoped API keys with only the rights they need. Then add rate limiting, IP allowlists and HTTPS on every endpoint, and let merchants rotate keys at any time.
On the server side, patch systems quickly and use firewalls and intrusion detection systems (IDS) to block bad traffic. Add DDoS protection so attack traffic cannot take checkout offline. In addition, split your network so that the public API can never talk straight to the signing systems.
8. Lock Down Your Domain, DNS and Checkout Page
If attackers take over your domain or DNS, they can serve a fake checkout page that shows their own wallet address. Buyers then pay the attacker, and the payment looks normal to them. So treat your domain like a wallet.
Turn on registrar lock and 2FA at your domain registrar, and enable DNSSEC. Use a strict Content Security Policy so that injected scripts cannot change the page. Also, always build the pay-to address on the server, never in the browser. Finally, show the amount and network clearly, since sending funds on the wrong chain is a common way buyers lose money.
9. Plan for Backups, Recovery and Breaches
Even with strong security, breaches or failures can still happen. A solid backup and recovery plan keeps your operations running. Back up transaction data and encrypted wallet backups to secure, off-site locations, and test a full restore at least twice a year.
Backups are only half the plan, though. Write down who does what in the first hour of an incident: who pauses withdrawals, who rotates keys, who tells merchants and who contacts law enforcement. Bitget’s case shows why this matters. In late September 2026, attackers breached a backend wallet system and spoofed transaction data. The exchange then paused withdrawals and reopened them in phases.
10. Educate Merchants and End Users on Security Practices
Technology alone can’t keep a platform safe; people play a huge role. Teach your merchants and users about phishing, fake support staff, password hygiene and wallet safety. For example, warn them about address poisoning. Here, a thief sends a tiny payment from a look-alike address and hopes it gets copied later.
Train your own staff as well, since social engineering often targets support and finance teams first. Share regular security updates, short tutorials and a clear rule: your team will never ask for a seed phrase or a 2FA code.
11. Keep Up with New Security Tools and Standards
The crypto industry evolves quickly, and so do attack methods. Stay ahead by following the latest security guides, smart contract audit standards and rule changes.
Newer tools can help, too. MPC signing, hardware security modules (HSMs), passkeys for login and zero-knowledge proofs can each make your platform harder to break. However, add them with care and test them well, since a new tool that is set up poorly adds risk rather than removing it.
12. Partner with Experts for Ongoing Security Checks
Security isn’t a one-off task; it never stops. Work with a crypto payment gateway development company or a compliance team for ongoing reviews and incident plans. These experts can help you find blind spots, manage new risks and keep a steady security posture all year.
Follow these 12 tips, and your crypto payment gateway can run with confidence. Users and merchants get payments that are safe, clear and easy to trust.
Security works best when it’s built into your payment system from day one, not added later. If you’re planning to develop one,
Explore our step-by-step guide on How to Create a Crypto Payment Gateway to see the full process, from design and setup to strong security.
Why Security Matters So Much for Crypto Payment Gateways in 2026
The crypto space keeps growing, and so do the threats behind it. As digital payments go mainstream, hackers find new ways to exploit weak spots in crypto payment gateways. From phishing to backend breaches, attacks have become far more advanced, leaving unprepared businesses at serious risk.
The numbers show the scale. Chainalysis found that hackers stole more than $3.4 billion from crypto services in 2025, and the Bybit attack alone took about $1.5 billion of it. The pace has not slowed in 2026. CertiK counted about $1.31 billion lost in the first half of the year. Then, it reported $1.26 billion lost across 247 incidents in the third quarter alone, led by the Bitget breach.
Notice where these losses come from. Most large thefts did not break the blockchain. Instead, they abused signing steps, backend systems, stolen keys and tricked staff. That is good news for gateway builders, because these are exactly the parts you control.
In a system built on trust, even one breach can damage your brand and merchant confidence. Payments on-chain are final, so stolen funds rarely come back. That’s why full protection isn’t just a tech need; it’s a business must.
So, what can businesses do to stay ahead? It starts with knowing the risks.
Common Security Risks in Crypto Payment Gateways
While crypto payment gateways enable fast and borderless payments, they also attract a wide range of cyber threats. Knowing the most common risks is the first step toward a secure setup for your users and merchants.
Here are the key weak spots that businesses should watch:
- Payment interception: Attackers try to grab data on the way, change payment details or swap the pay-to address.
- API weak spots: Weak or unprotected APIs can give hackers access to payment data and user details.
- Wallet key exposure: Poor key handling can lead to the loss or theft of private keys, which gives attackers full control of the funds.
- Smart contract bugs: Coding errors or unaudited contracts can open backdoors in on-chain payment systems.
- Insider attacks: Staff with admin access might misuse it for their own gain or to cause harm.
- Fake payments and double spends: Forged “paid” notices, replayed webhooks or payments credited too early can release goods for nothing.
- Phishing and social engineering: Fake support staff, fake login pages and tricked signers remain the most common way in.
- Tainted or frozen funds: Payments from sanctioned or hacked wallets can trigger issuer freezes or legal trouble.
Key Threats and Preventive Measures
| Threat | Preventive measure |
| Payment interception | Use TLS encryption, build the pay-to address on the server and confirm each payment on-chain. |
| API weak spots | Test APIs often, use scoped keys and tokens, and limit access with role-based permissions. |
| Wallet key exposure | Keep most funds in cold storage and use multi-sig or MPC signing, with keys held in HSMs. |
| Smart contract bugs | Run third-party smart contract audits and ongoing code reviews. |
| Insider attacks | Use role-based access control (RBAC), two-person approval for payouts and admin activity logs. |
| Fake payments and double spends | Sign webhooks, check them on every call and set confirmations per chain. |
| Phishing and social engineering | Use hardware keys for 2FA, train staff and confirm large transfers on a second device. |
| Tainted or frozen funds | Screen addresses against sanctions and hack lists before you credit or pay out. |
By fixing these weak spots early, businesses can prevent costly breaches and keep their payment system strong.
Custodial vs Non-Custodial: How Your Model Changes the Risk
Your custody model decides which of these risks you carry. A custodial gateway holds merchant funds, then converts and pays them out. It can offer fiat payouts and easy refunds. However, it becomes a target for hackers, and it needs a licence in most markets.
A non-custodial gateway sends each payment straight to the merchant’s own wallet. You never hold the funds, so there is far less to steal. On the other hand, the merchant must protect their own keys, and fiat payouts are harder to offer. Many gateways mix both models, or use MPC to split control between the merchant and the gateway. Our guide to the features of a crypto payment gateway shows how to choose.
Rules and Compliance to Secure Your Crypto Payment Gateway
As crypto adoption grows, so does the focus on compliance. Lawmakers around the world are making rules stricter to fight dirty money, fraud and other crime. For a gateway, following the rules isn’t just about dodging fines; it’s about trust and a business that lasts.
GDPR: The EU Data Law
If your platform serves users in the EU, GDPR applies. It requires you to protect user data, get clear consent and explain how you store and use it. Serious breaches of the rules can bring fines of up to EUR 20 million or 4% of global yearly turnover, whichever is higher.
KYC and AML Checks
These rules form the backbone of crypto security and trust. KYC and AML checks help you confirm who users are, track odd payments and stop illegal transfers. Many leading gateways use automated checks so that compliance does not slow down the user.
MiCA in the EU
In the EU, firms that hold, swap or transfer crypto for clients need a CASP licence under MiCA. The grace periods in each member state ended by 1 July 2026 at the latest. A licence also brings rules on how you hold funds, guard your IT and report breaches.
FATF (Financial Action Task Force) Guidelines and the Travel Rule
The FATF Travel Rule requires virtual asset service providers (VASPs) to share sender and receiver details on transfers. The FATF standard sets a USD/EUR 1,000 threshold, and many countries follow it. In the EU, the Transfer of Funds rules have applied to every crypto transfer between firms since 30 December 2024. The FATF also revised Recommendation 16 on payment transparency in June 2025, with full compliance due by the end of 2030.
Stablecoin Rules (US GENIUS Act)
The GENIUS Act, signed on 18 July 2025, set federal rules for payment stablecoin issuers. It takes effect by 18 January 2027 at the latest. So gateways should favour stablecoins from licensed issuers and plan for issuer freezes.
Local Rules by Country
Crypto compliance also varies by region. In the US, most gateways that move value for others register with FinCEN as money services businesses. In India, crypto firms have had to report to FIU-IND under the PMLA since March 2023, and they must register with it. And if your gateway also takes card payments for crypto on-ramps, PCI DSS rules apply to that card data.
By following these rules, businesses not only lower their legal risk but also make their platform more trusted. With security and compliance working together, the base of a trustworthy crypto payment system becomes stronger than ever.
Once your gateway meets high security and compliance standards, the next step is the budget. Read our breakdown of Cost to Create a Crypto Payment Gateway – covering key cost factors, build phases and ways to save.
Crypto Payment Gateway Security Checklist Before You Go Live
Tips are only useful if you test them. Before launch, ask your team to prove each point below in the sandbox or on a staging system.
- Fake payment test: Send a forged and a replayed webhook. Both must be rejected.
- Wrong amount test: Pay too little, too much and too late. Each case must be flagged, topped up or refunded.
- Confirmation test: Check that large payments wait for more confirmations than small ones.
- Payout test: Try a payout to an address that is not whitelisted. It must be blocked or held for a second approval.
- Screening test: Send funds from a test address on your block list. They must be held for review.
- Access test: Confirm that a support account cannot move funds or change payout addresses.
- Restore drill: Restore the system from backups and time how long it takes.
- Incident drill: Run a one-hour desk drill for a hot wallet breach, from pausing withdrawals to telling merchants.
- External audit: Get an outside pen test and a smart contract audit, and fix each high-risk finding before launch.
If you plan to resell the platform under your own brand, run the same checks on a white label crypto payment gateway before you sign.
Build a Secure Crypto Payment Gateway with Coinsclone
Coinsclone has been building crypto products since 2018 and has delivered 350+ platforms for 200+ clients across 20 industries. Our crypto payment gateways come with cold storage and MPC or multi-sig signing, signed webhooks, address screening and ready compliance tools. A standard gateway takes 6 to 9 weeks to launch, and a build with fiat settlement takes 10 to 14 weeks. Share your plan with our crypto payment gateway development team, and we will map the security controls to your launch.
Final Thoughts
Security isn’t a one-time setup; it’s an ongoing process. In 2026 and beyond, a safe crypto payment gateway needs constant care, frequent audits and a safety-first mindset.
The crypto world thrives on new ideas, but new ideas without security can end in disaster. Pair strong tech safeguards with clear compliance, and your payment gateway can stand firm as cyber threats change.
In short, a secure crypto payment gateway is more than a feature; it’s your brand’s promise of trust in the crypto world.
See How Our Proven System Can Secure Your Crypto Payment Gateway
Crypto Payment Gateway Development — done right.
-
Advanced Security Stack : Multi-sig wallets, 2FA, SSL, and DDoS protection by default.
-
Compliance-Ready : Built-in KYC/AML modules to meet global regulations.
-
Fraud Prevention : Real-time monitoring and risk scoring to block suspicious transactions.
-
Data Protection : End-to-end encryption for all payment and user data.
Get a free security audit checklist to evaluate your payment system’s safety.
Book a Free Demo to learn how our Crypto Payment Gateway Development Solution helps you launch faster — and safer.
Frequently Asked Questions
Are crypto payments safe for businesses?
Yes, if the gateway and the business follow good safety habits. On-chain payments cannot be charged back, which removes card fraud. However, the business must protect its keys, check each payment on-chain and screen funds. The main risks sit in wallets, logins and back-office systems, not in the blockchain itself.
What is the safest way to accept crypto payments?
Use a licensed or well-audited gateway, or build one with cold storage, multi-sig or MPC signing, signed webhooks and address screening. Wait for enough confirmations before you ship goods. Many merchants also convert payments to stablecoins or local currency at once to avoid price swings.
How do I protect my crypto wallet?
Keep most funds in cold storage, use a hardware key for 2FA and never share your seed phrase. For business wallets, add multi-sig or MPC so that no single person can move funds. Our guide on crypto wallet security covers the details.
Can crypto transactions be reversed?
No. Once a blockchain transfer is confirmed, it is final. A gateway can only send a refund as a new transaction. That is why gateways must check each payment carefully before crediting it, and why a clear refund flow for wrong amounts matters.
What are the biggest crypto payment risks?
The biggest risks are stolen or exposed private keys, phishing and social engineering, weak APIs, fake payment notices and funds from sanctioned or hacked wallets. Price swings are a business risk as well. Most of these can be cut sharply with the 12 tips in this guide.